What You Feed the Model Is the Model
A practical piece on why model behavior is inseparable from the quality, framing, and structure of the input and context you provide.
Read on DevArmor →
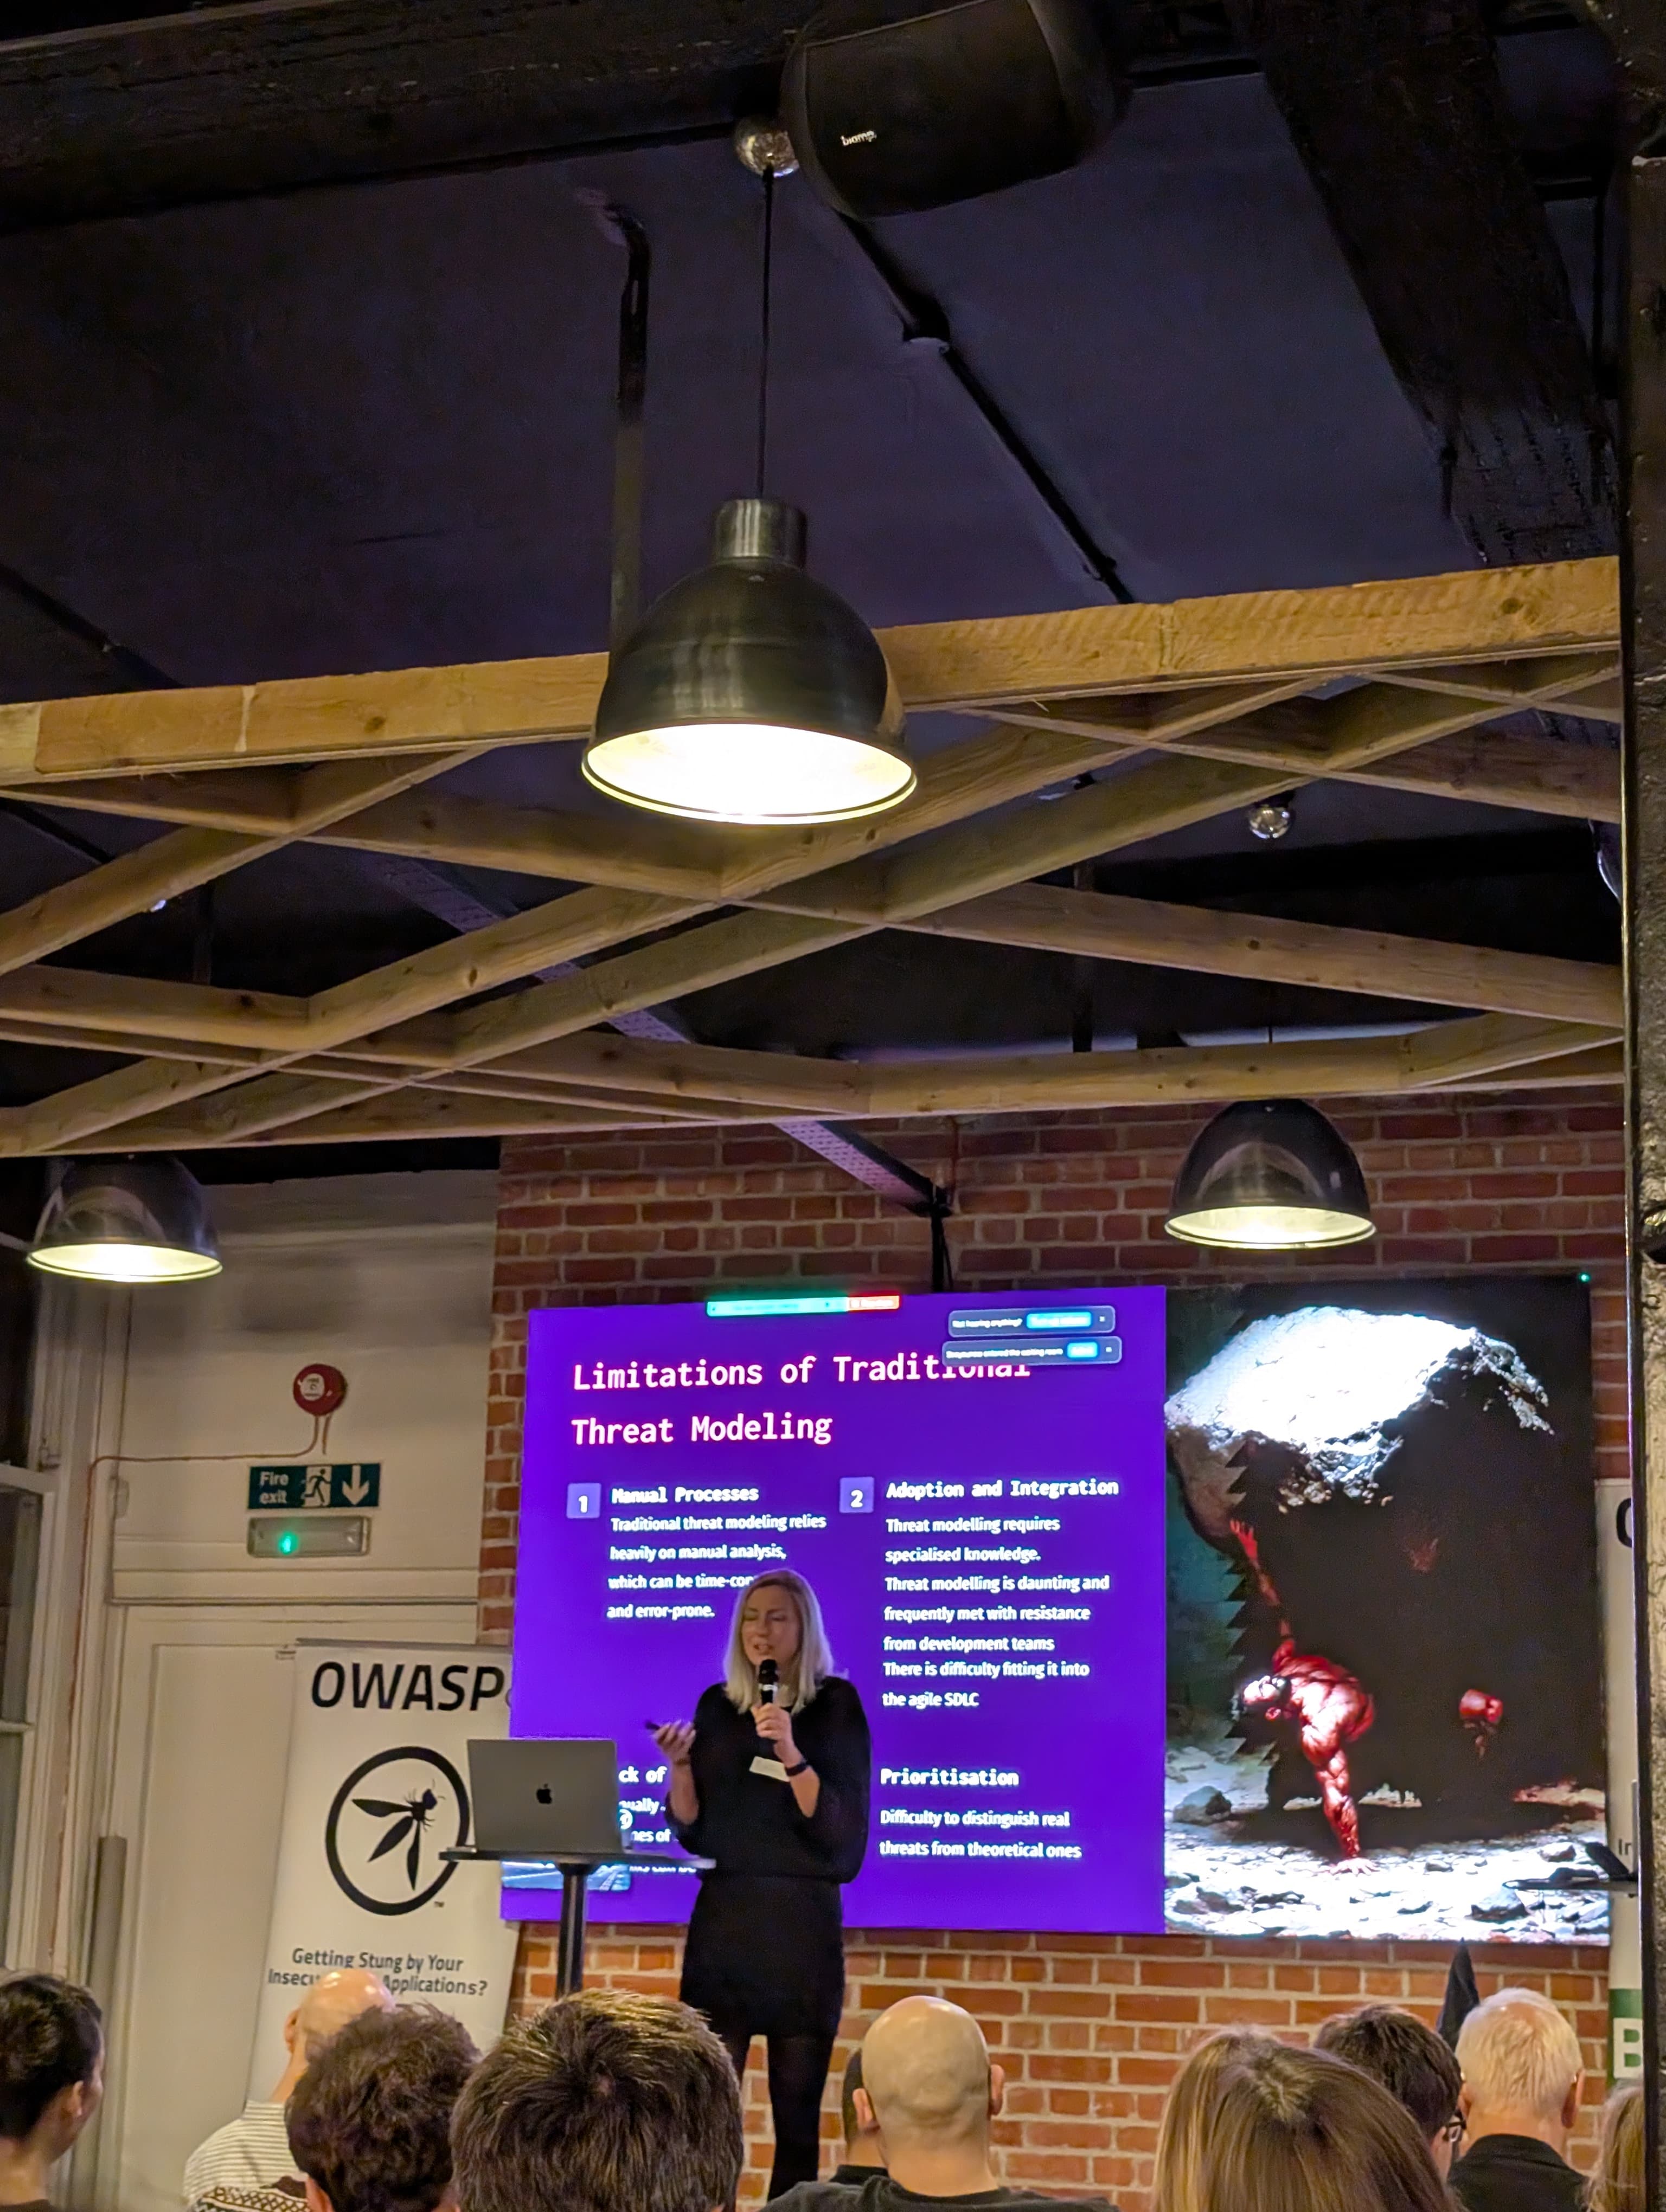
My journey into cybersecurity is unconventional. I started my career as an Emergency Medicine Doctor in Croatia, later moving to the UK to continue my specialty training with the NHS. The high-pressure environment of the ER taught me to think systematically about complex, ambiguous problems — and to build protocols that work when everything is on fire. Those same skills now drive how I approach incident response playbooks and security architecture.
Today, I serve as Director of Security, AI and Internal Technology at Flagstone and Fractional Head of Product at DevArmor. I apply diagnostic thinking from medicine to threat modeling — the parallels are striking: differential diagnosis is just threat modeling for the human body. Both fields require pattern recognition, risk assessment under uncertainty, and protecting what matters most.
I'm an OWASP Project Co-Leader for the Threat Model Library — the first open-source, structured, peer-reviewed threat modeling dataset. I also co-lead the Threat Modelling Use Cases working group at the Linux Foundation AI & Data. My mission is to democratise security knowledge and make threat modeling accessible to everyone.
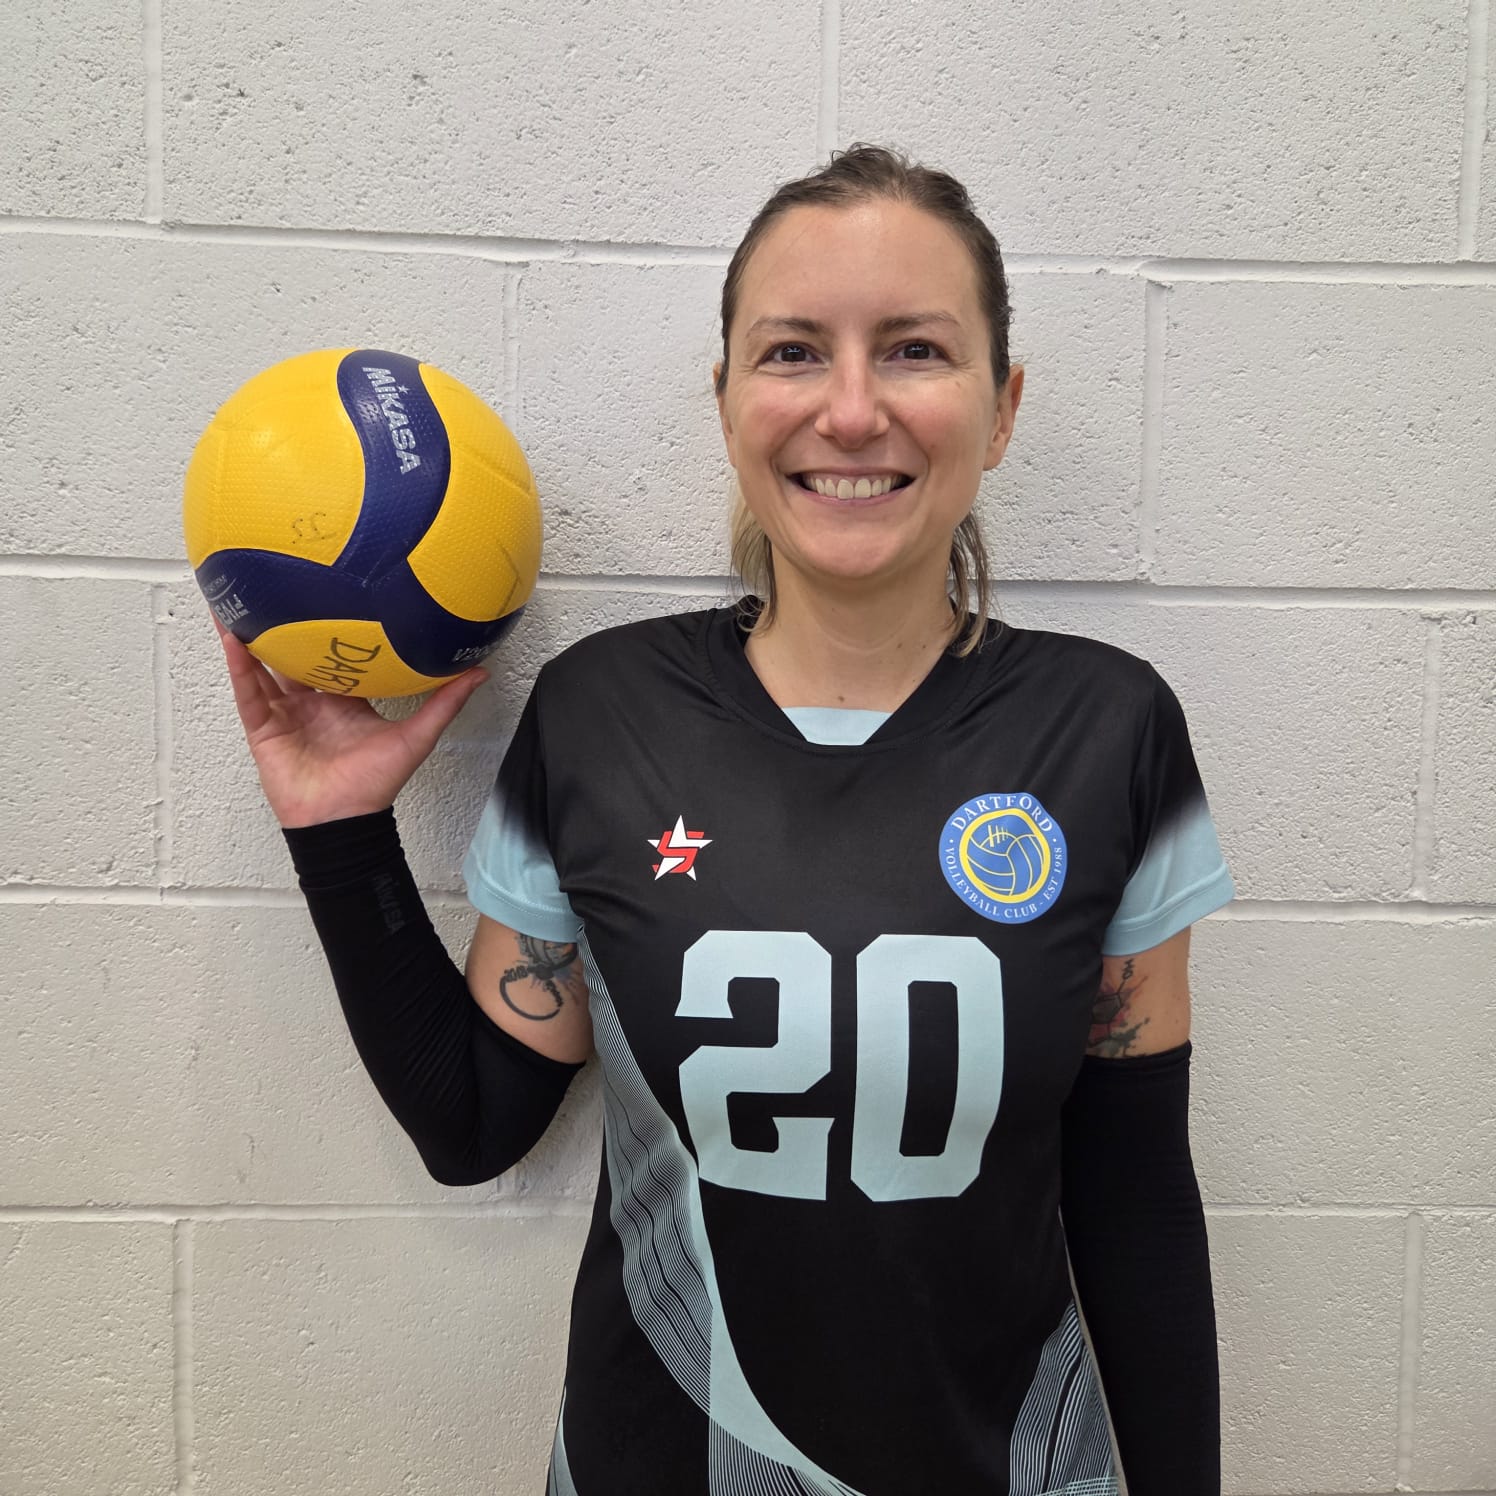
Outside of work, alongside with my mother, I co-founded a non-profit in Croatia called DIP, focused on community inclusion — running workshops, activities and mentoring programs for young people with learning disabilities and various types of neurodiversity. I also compete in volleyball in the NVL and London League, and beach volleyball in the UKBT.
Director of Security, AI & Internal Technology at Flagstone

Threat Model Library Project Co-Leader — first open-source, peer-reviewed TM dataset
Threat Modelling Use Cases Working Group Co-Lead

Fractional Head of Product — building security tooling for developers

Non-profit co-founder — community inclusion programs for young people with learning disabilities and neurodiversity
Emergency Medicine Doctor trained in Croatia and the UK NHS
Competitive volleyball player — NVL, London League & UKBT beach volleyball
 Who am I
 On the court
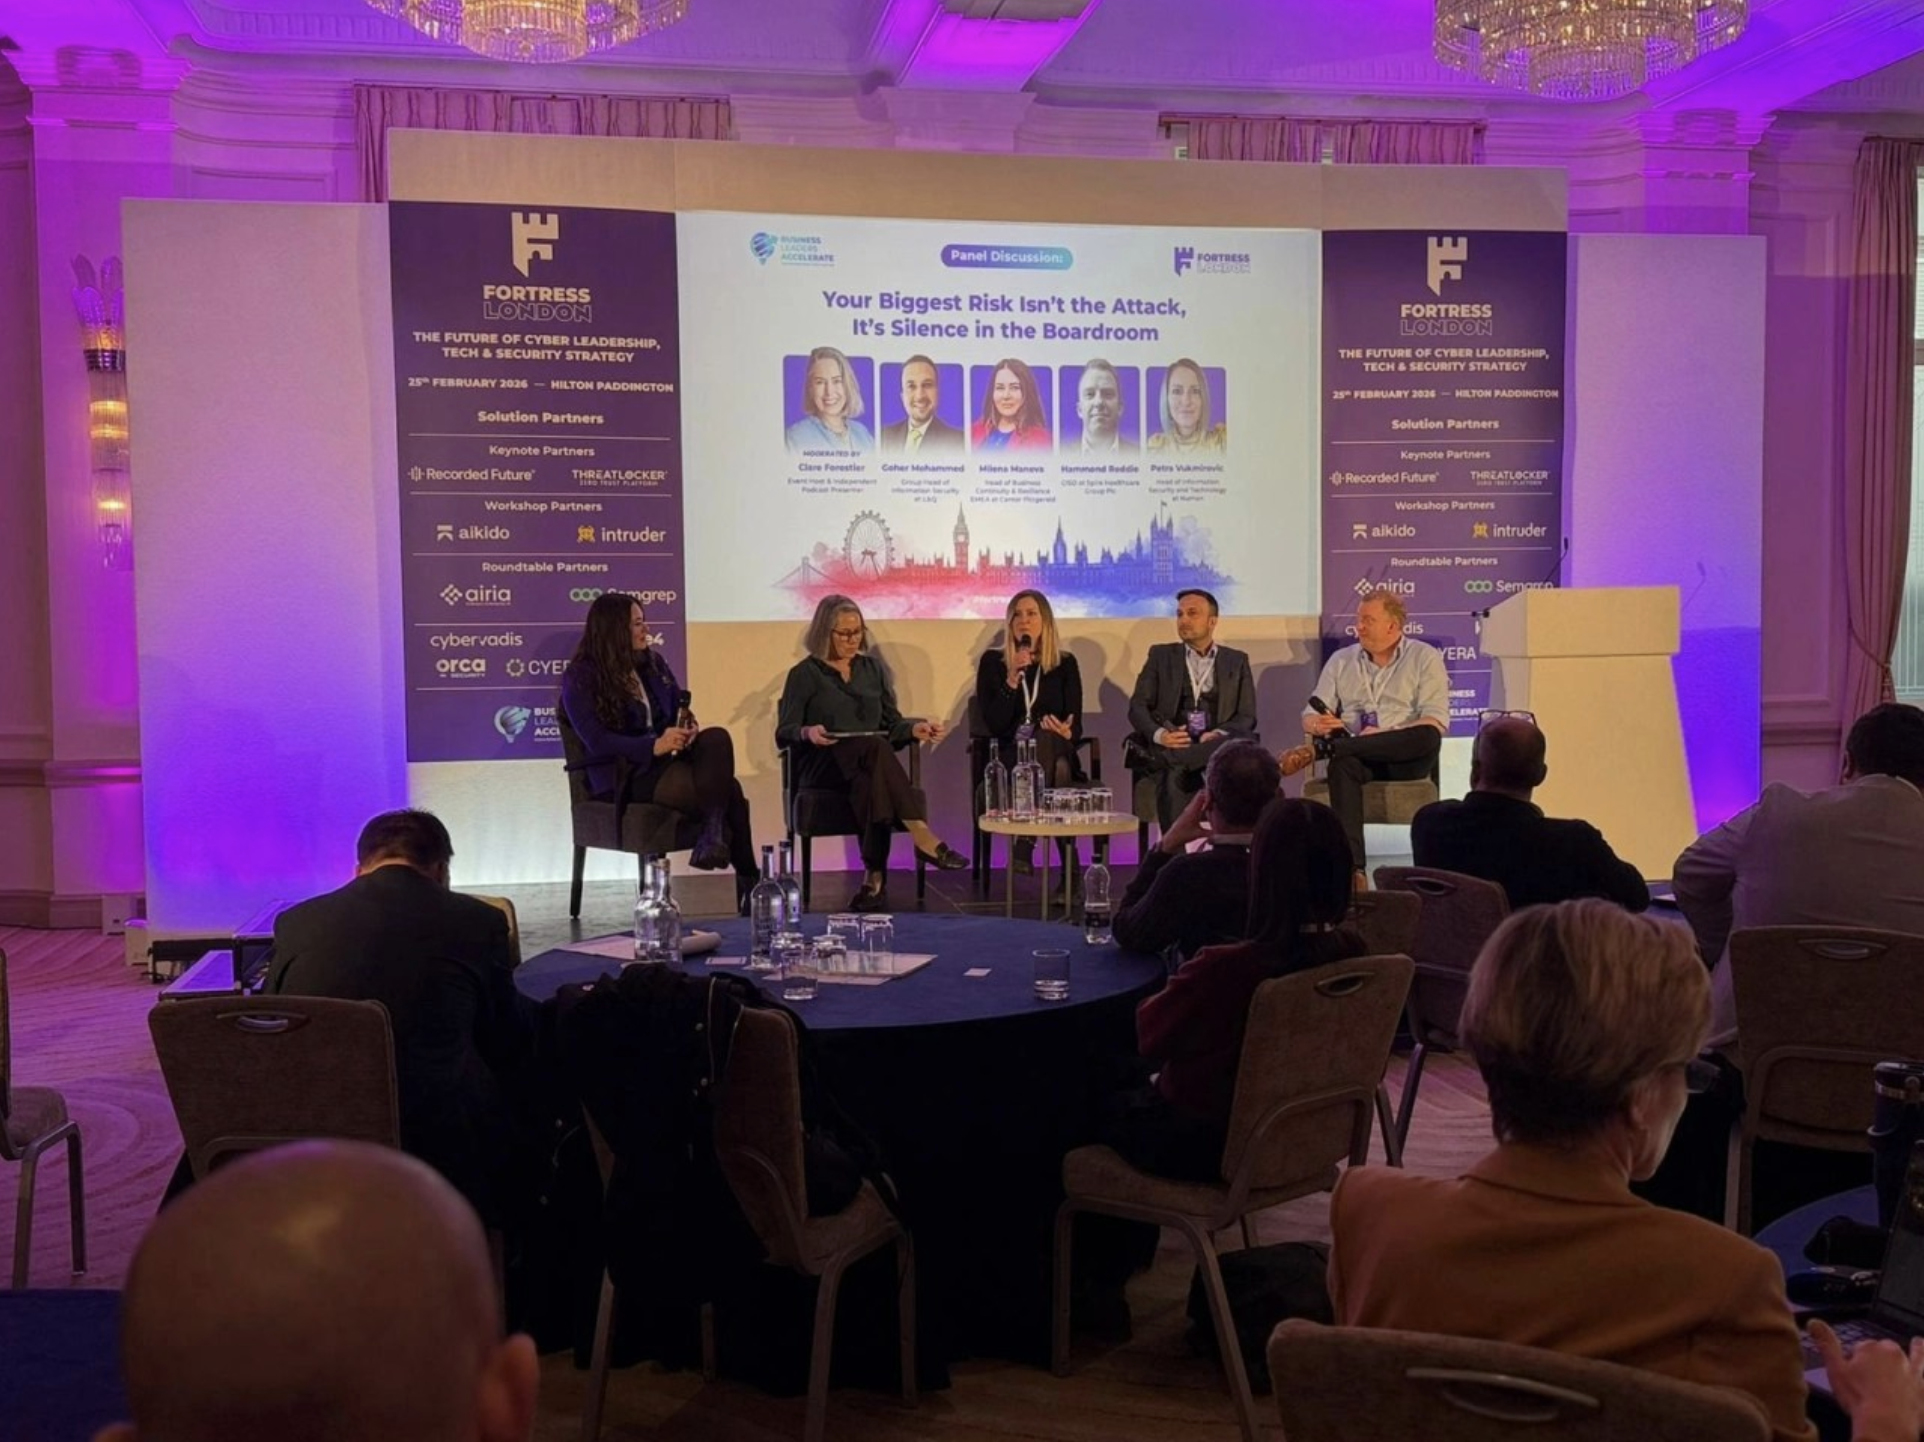
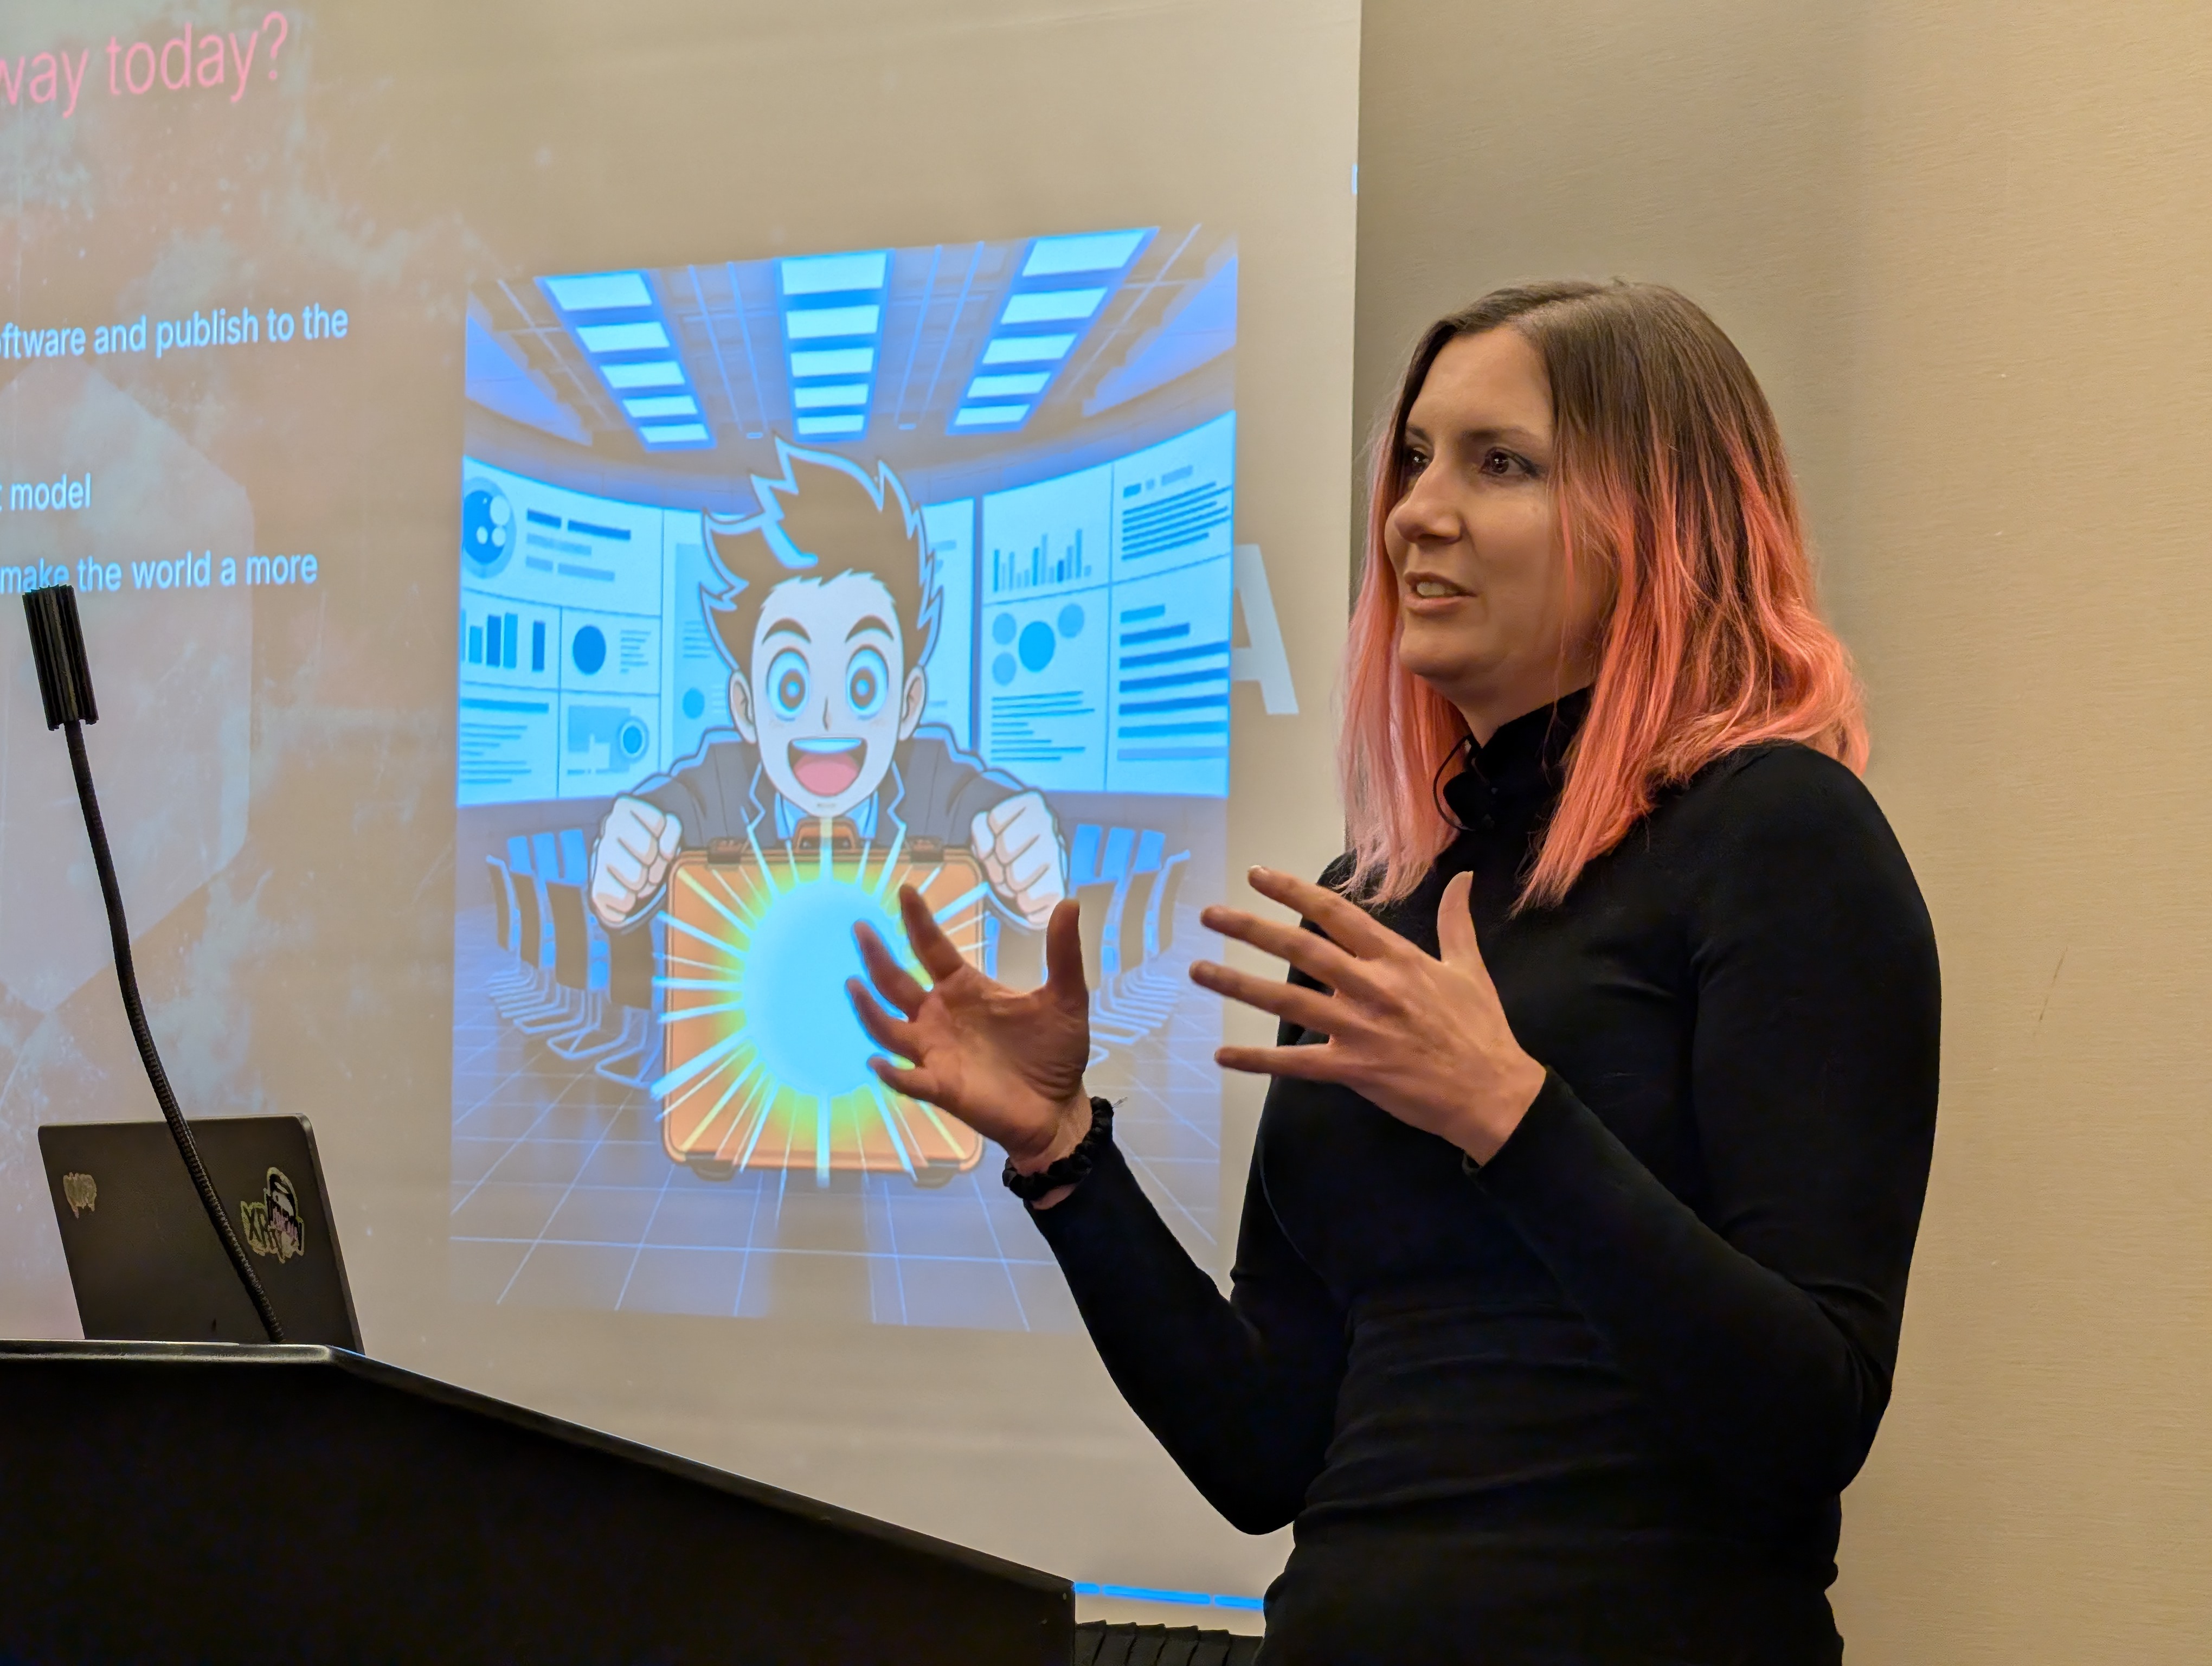
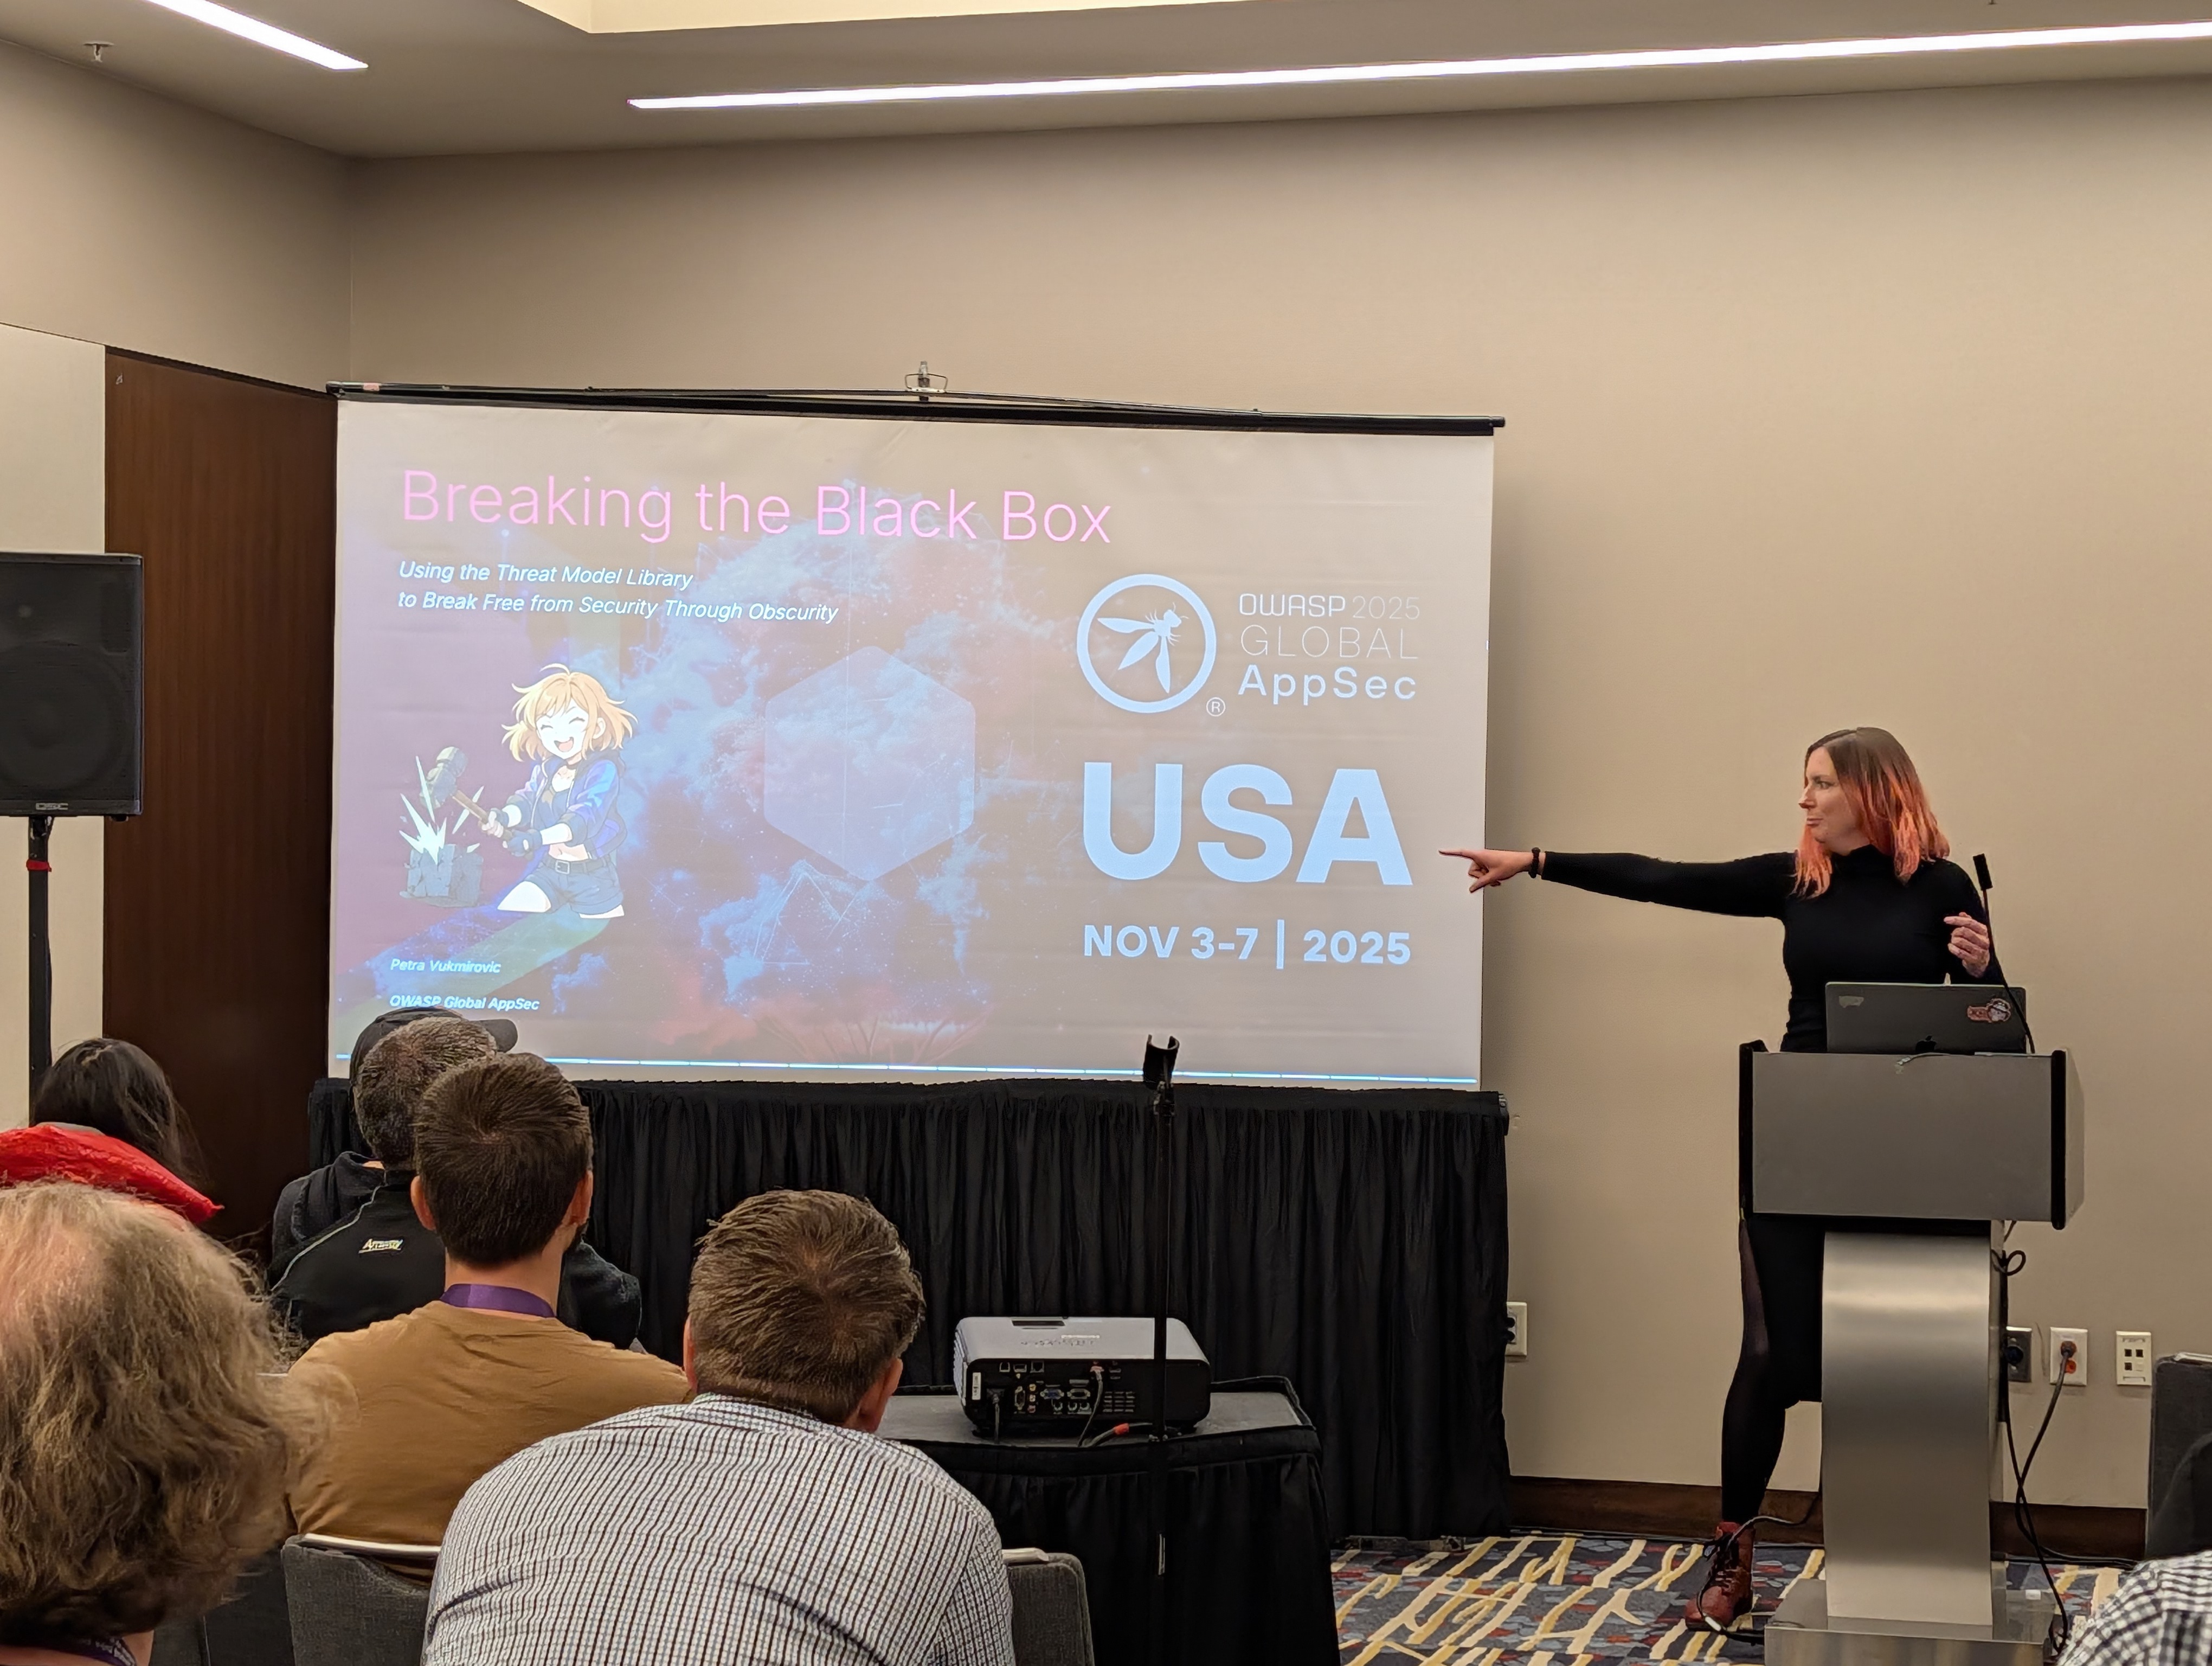
← scroll for more →
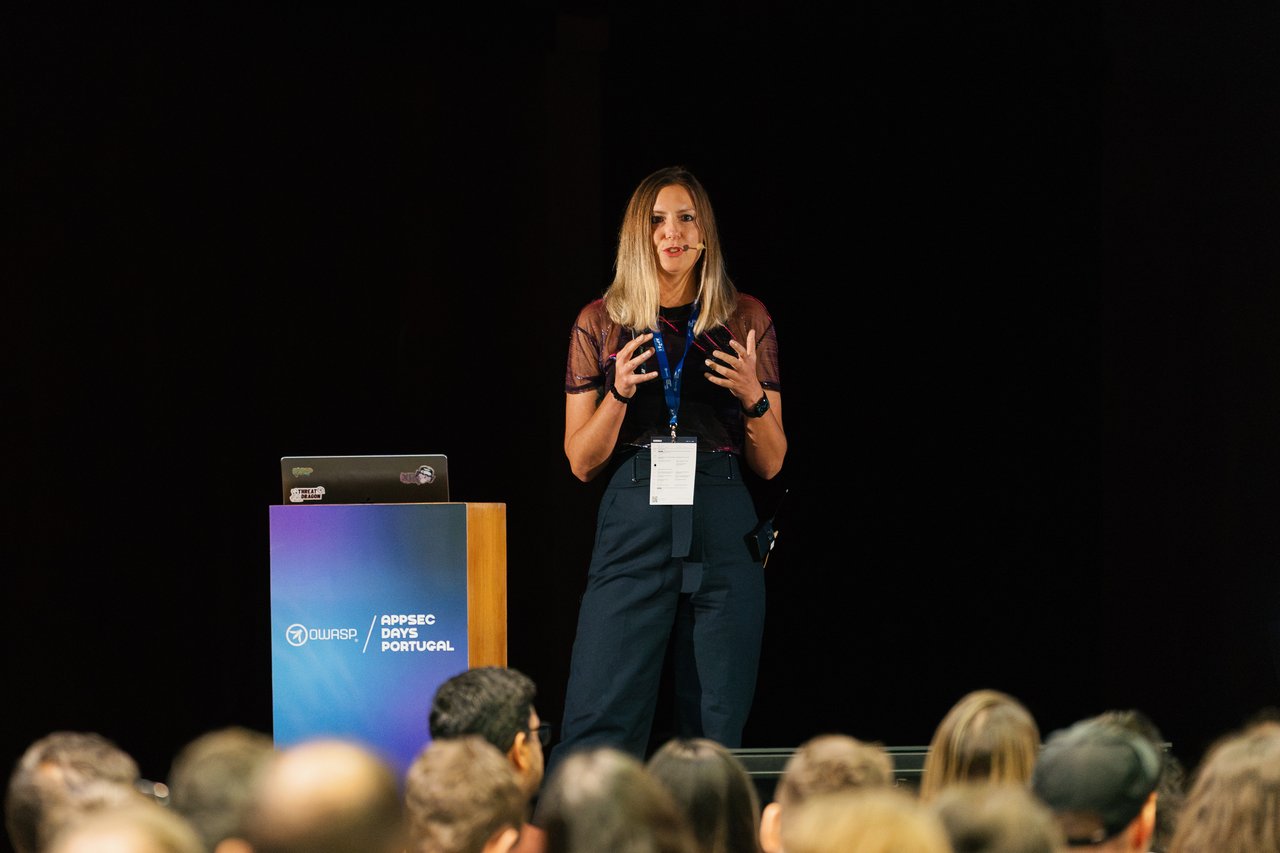
Closing keynote at OWASP AppSec Days Portugal — Porto, Portugal, 2026
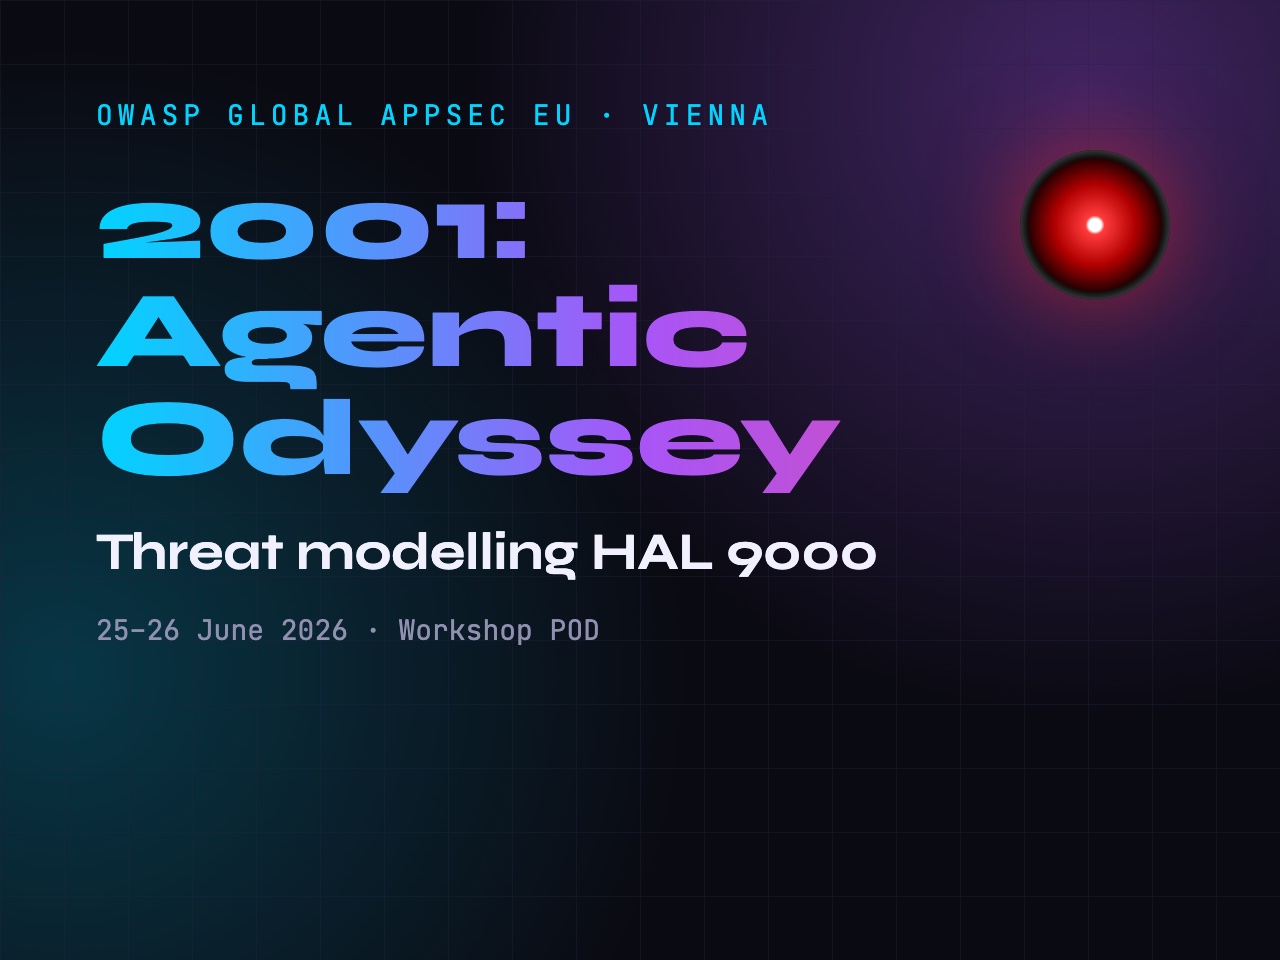
Hands-on drop-in workshop threat modelling HAL 9000 as a modern agentic AI system and turning attack trees into fault tree analysis and test ideas. Run as a POD at OWASP Global AppSec EU — Vienna, June 25–26, 2026, and at the OWASP Foundation workshop space at DEF CON 34 — Las Vegas, August 9, 2026
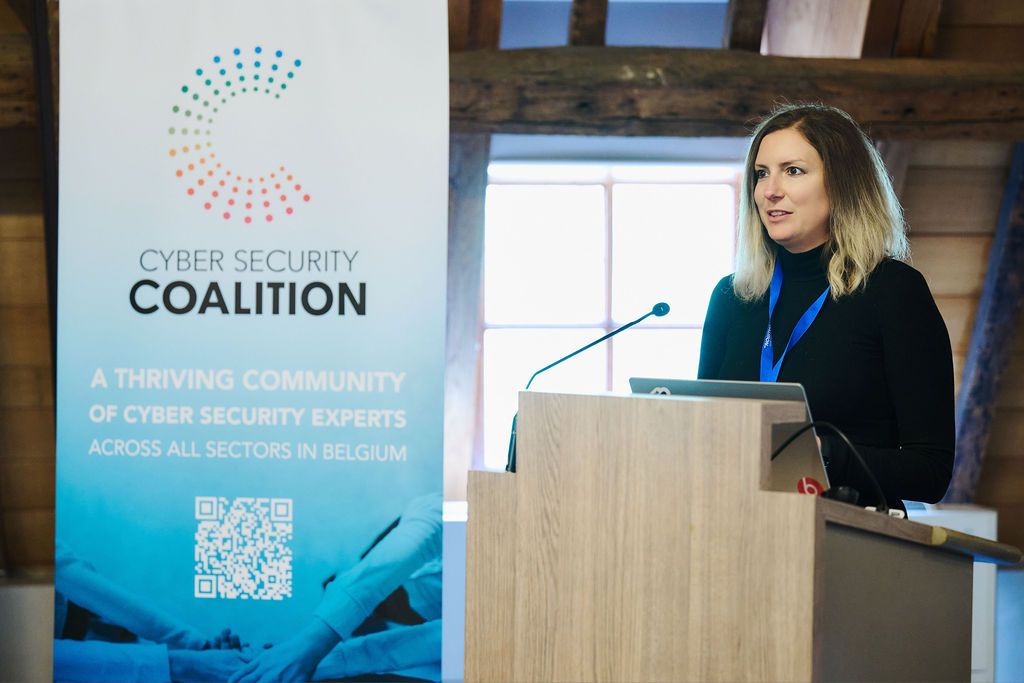
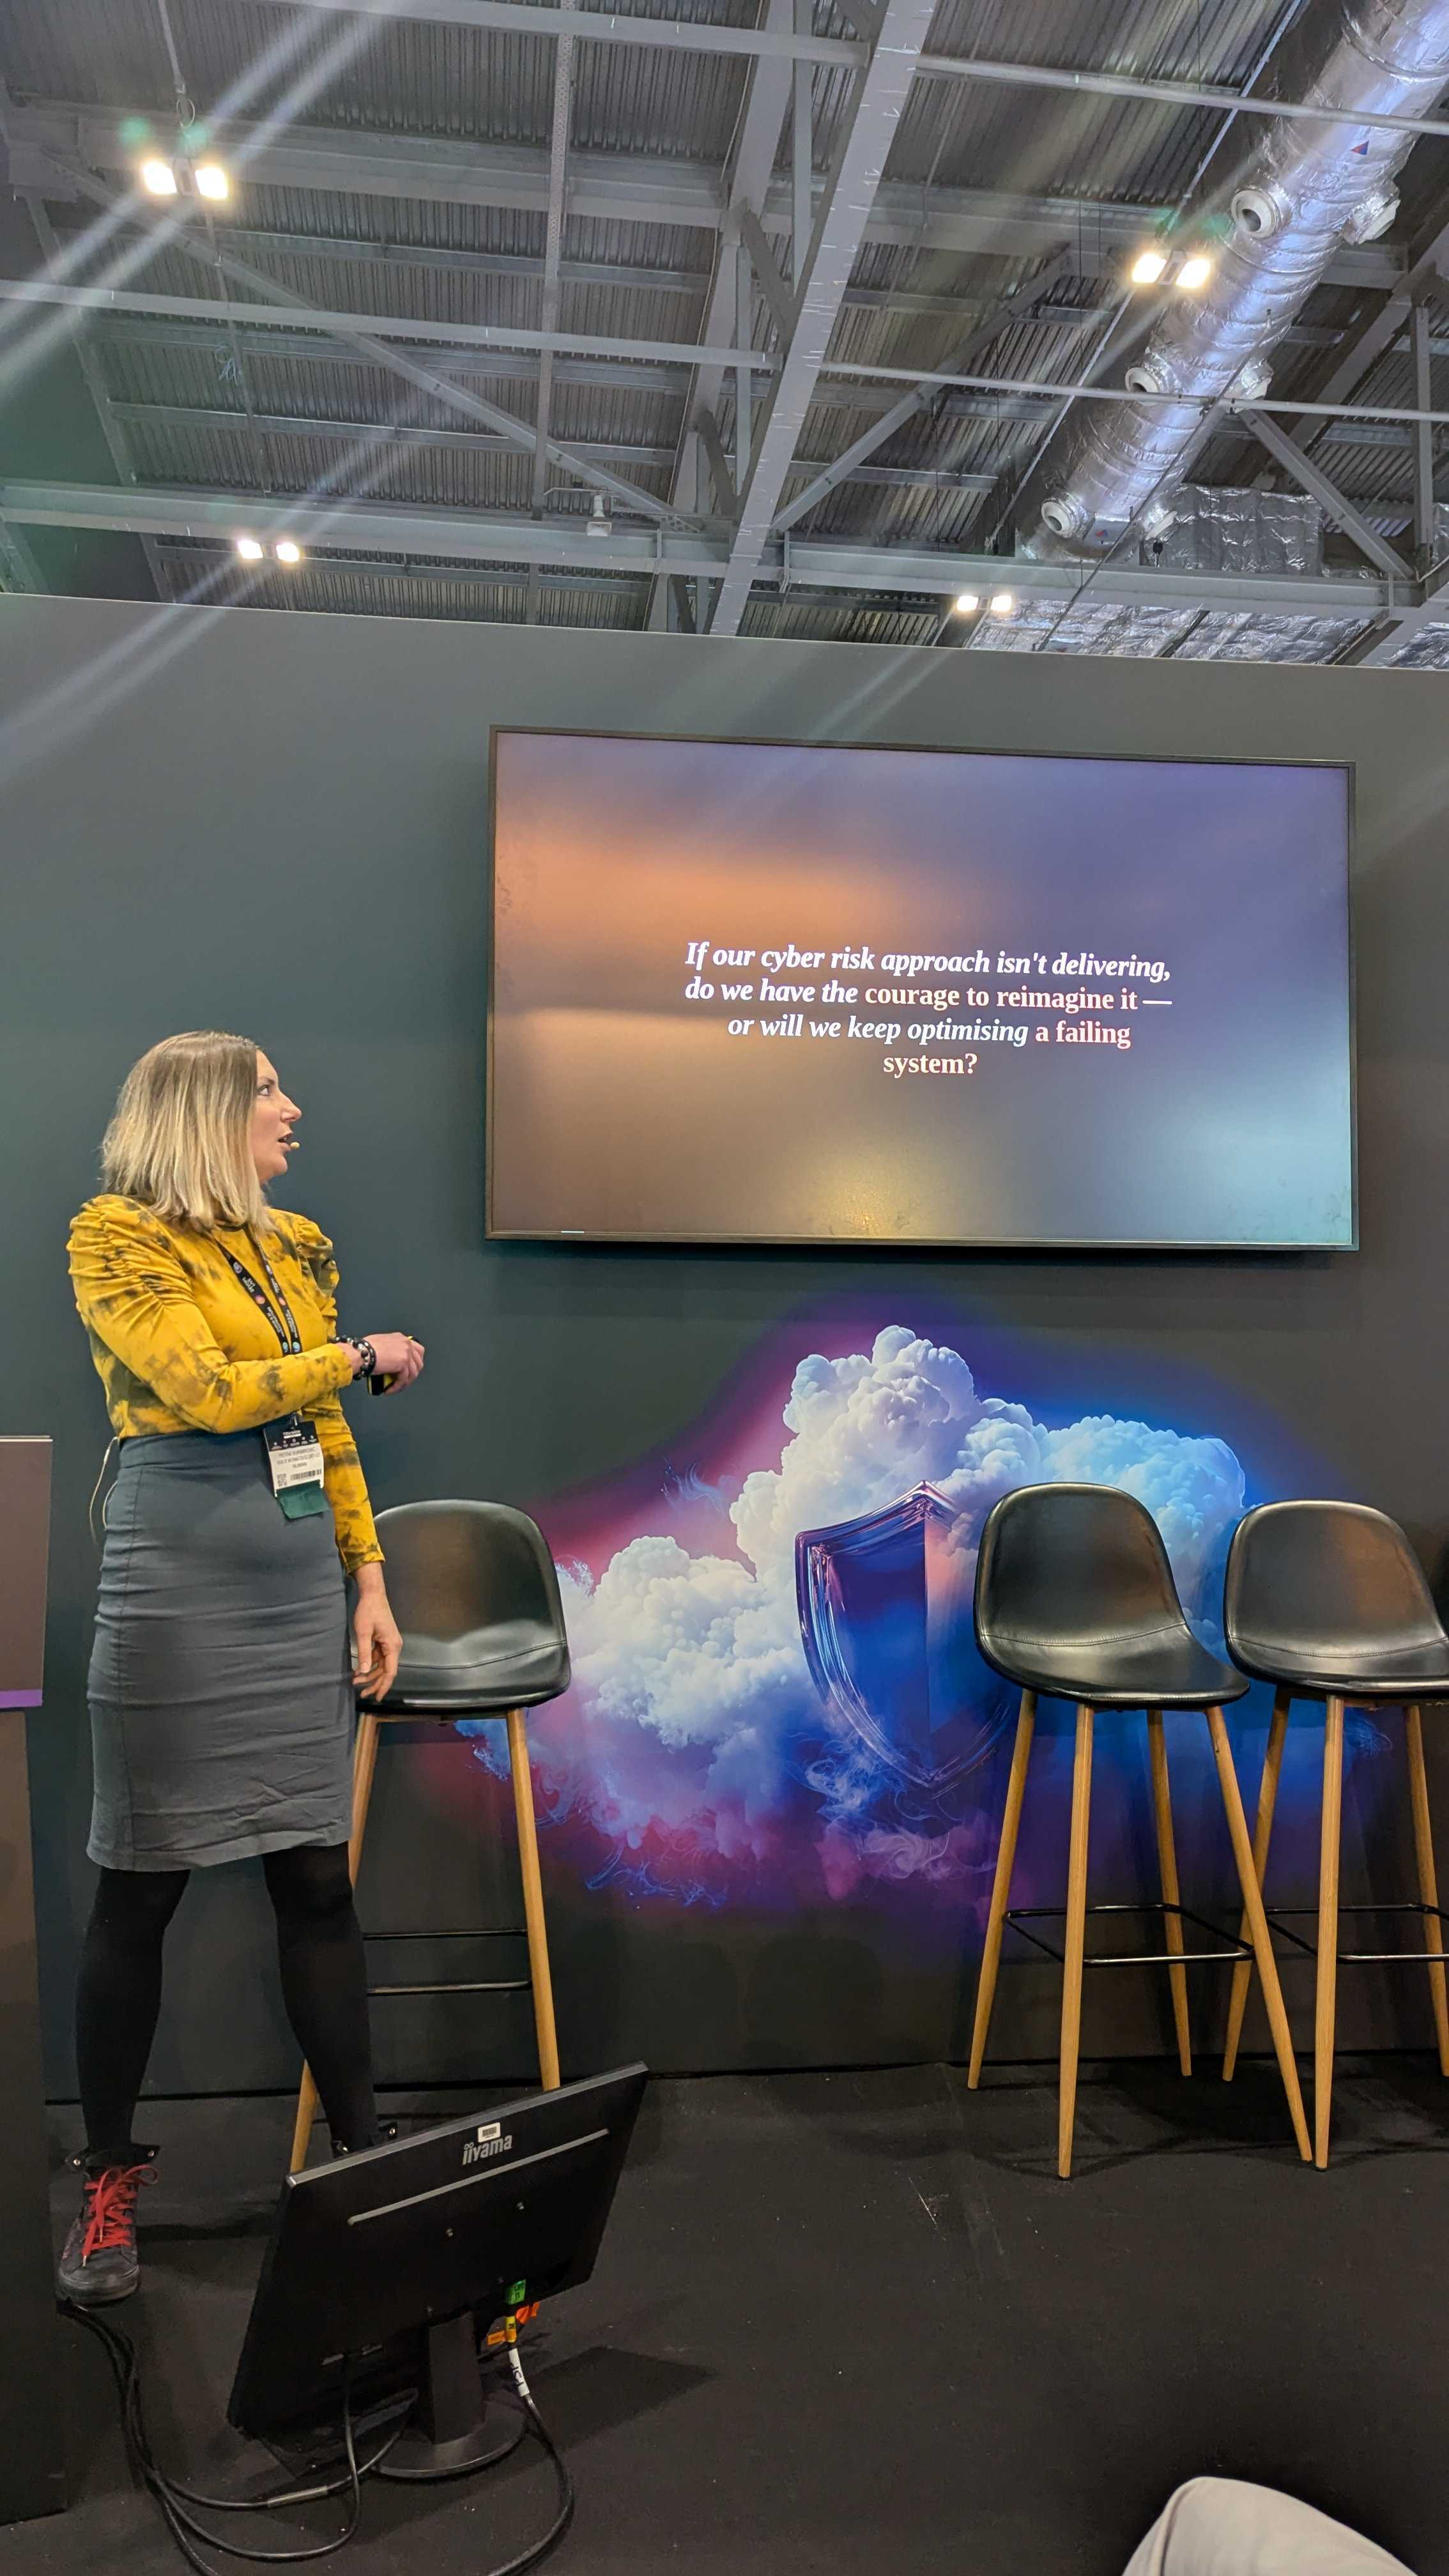
Presented at London Tech Show 2026 and the Belgian Cyber Security Coalition × SecAppDev Application Security Experience Sharing Day — Faculty Club, Leuven, Belgium, 4 June 2026
OWASP Global AppSec USA 2025 — Washington D.C., Nov 3–7
OWASP Global AppSec Barcelona — May 29th, 2025
Presented at OWASP London Chapter on October 31, 2024 and London DevSecOps Meetup on April 16, 2025
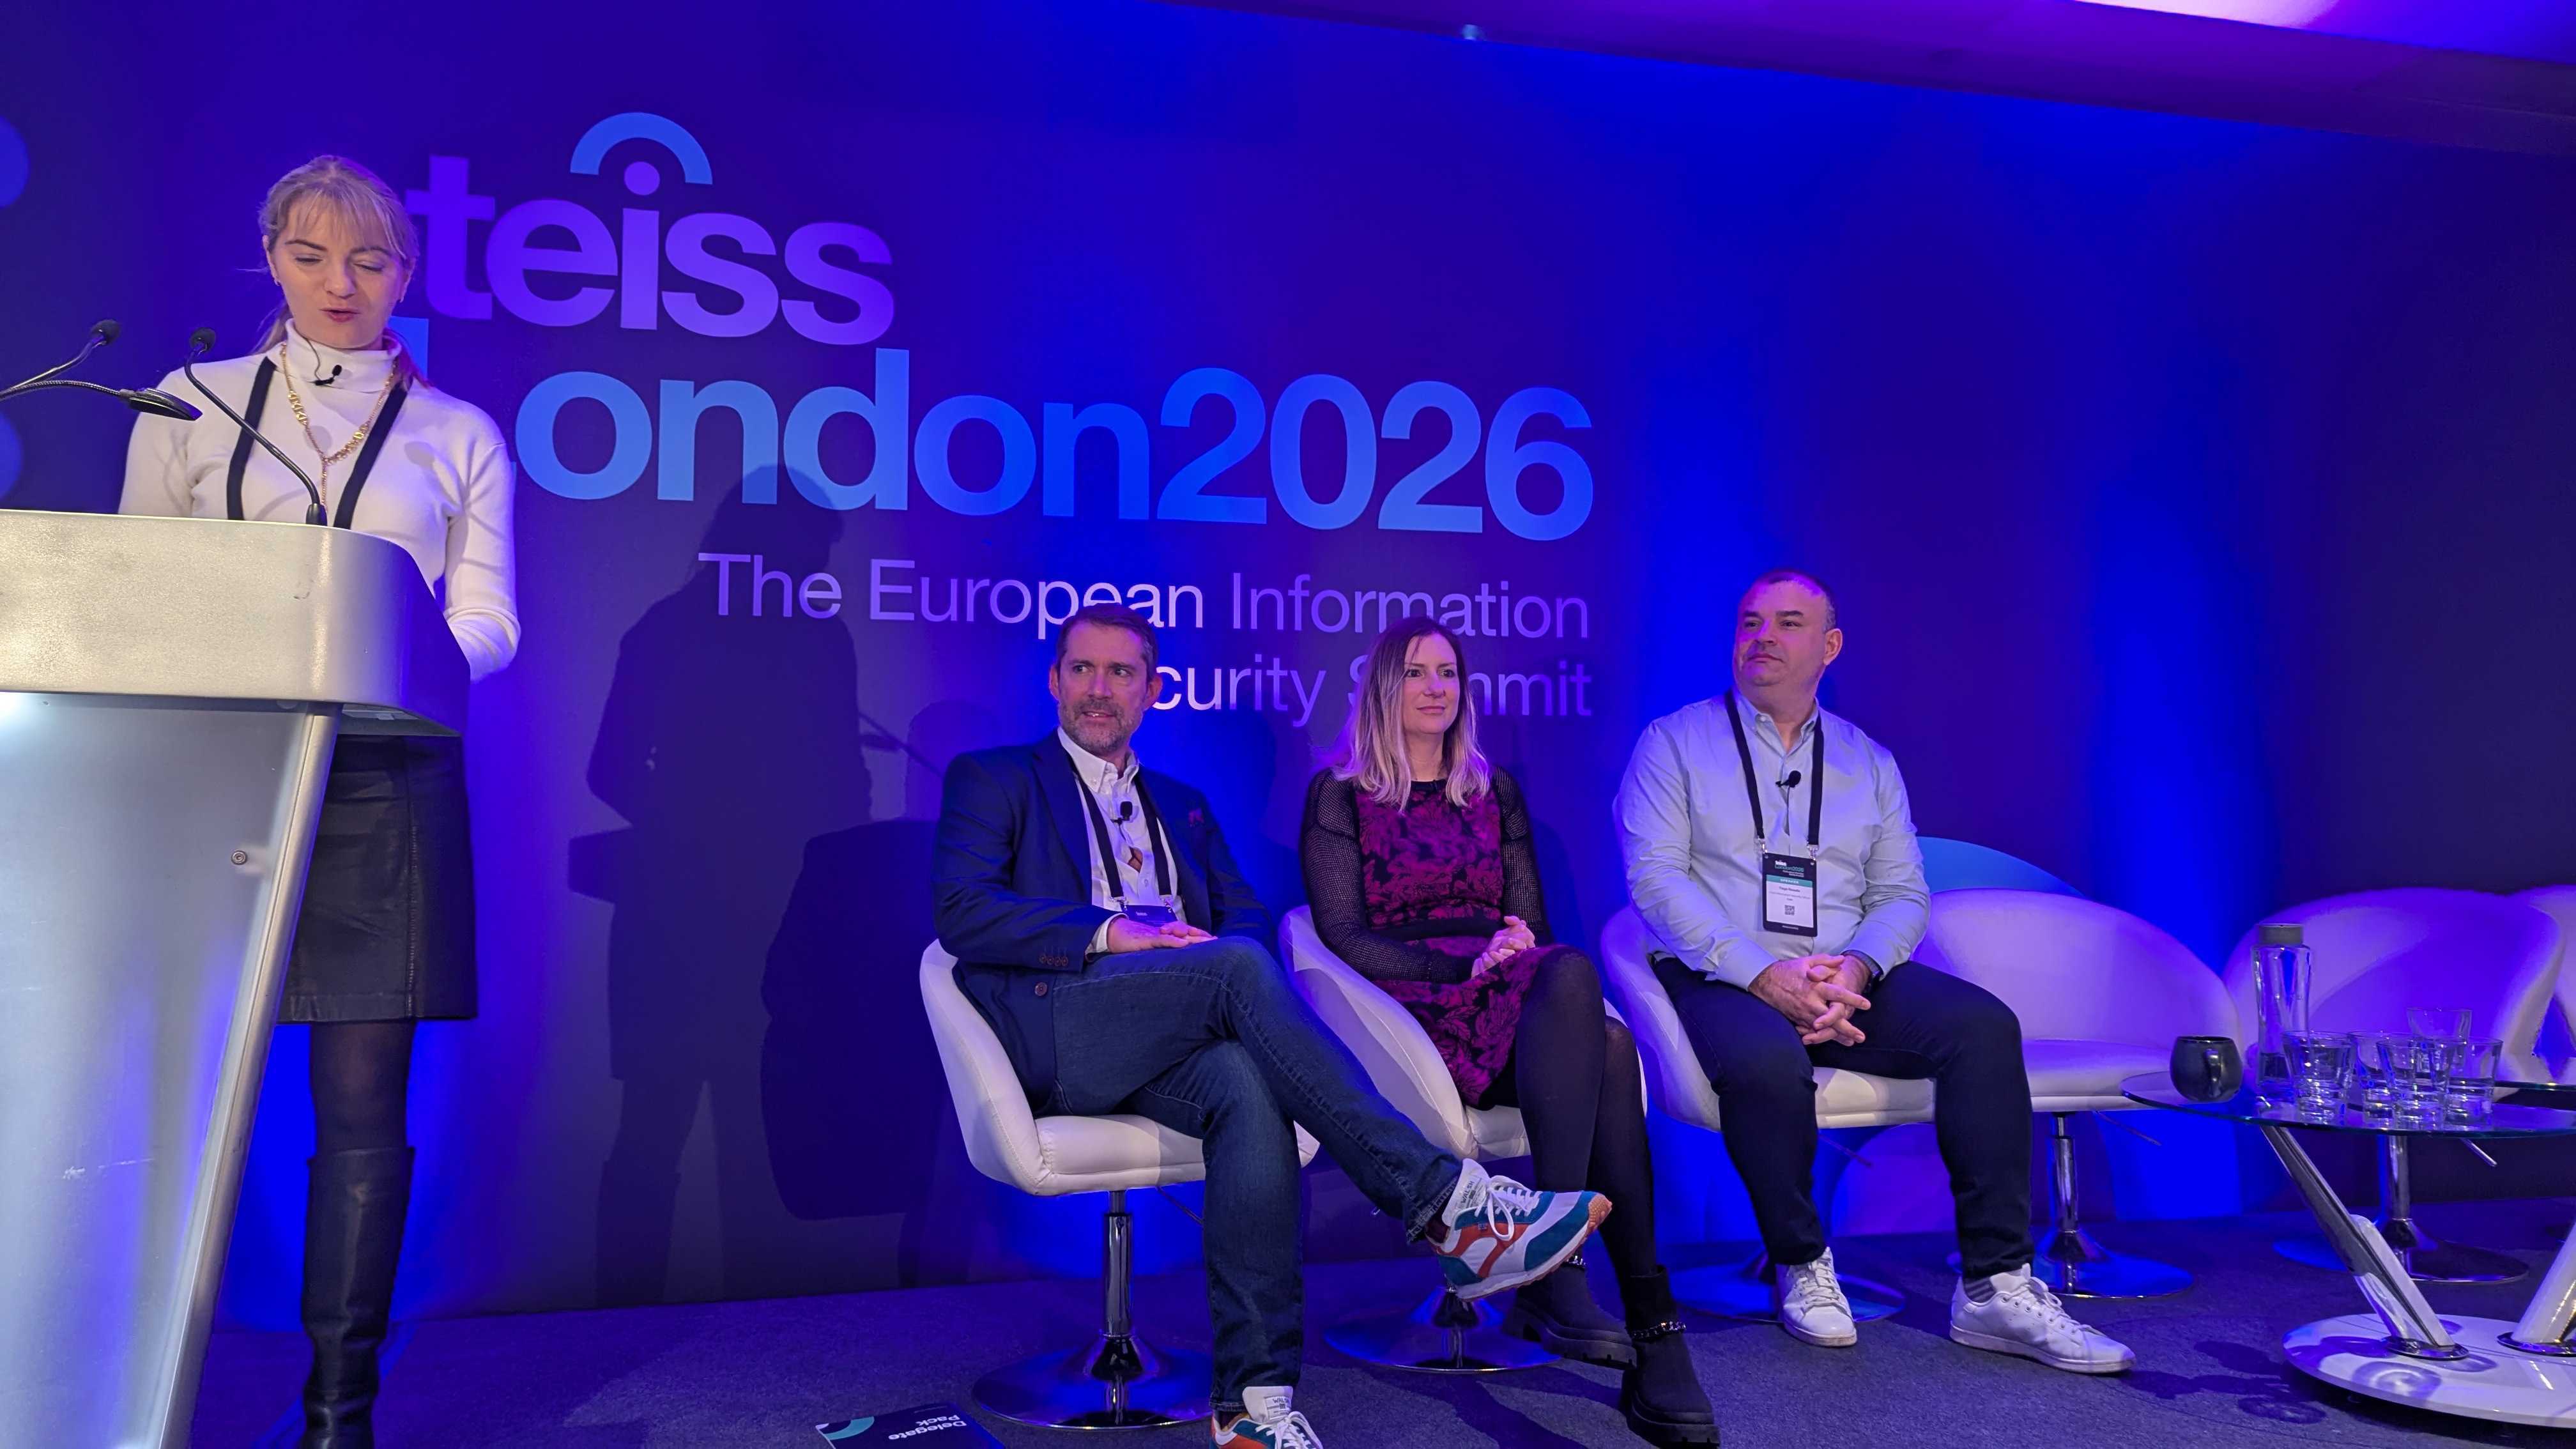
Selected panel appearances focused on leadership, threat intelligence, AI in security, resilience, and inclusive security practice.
OWASP Global AppSec USA 2026 — San Francisco, USA
PanelOWASP Global AppSec USA 2026 — San Francisco, USA
KeynoteOWASP Global AppSec USA 2026 — San Francisco, USA
ConferenceMy writing and speaking style is clear, direct, witty, and grounded in real-world practice. I focus on making complex security topics understandable, challenging assumptions that no longer hold, and turning abstract ideas into practical, thought-provoking insight. Whether through talks or blog posts, my aim is to give people something useful to question, rethink, and apply.

A practical piece on why model behavior is inseparable from the quality, framing, and structure of the input and context you provide.
Read on DevArmor →A candid, humorous look at the hiring manager’s view of LinkedIn profiles and the recurring patterns that show up during security hiring.
Read on Medium →Key takeaways from the influential DevOps novel and how to apply them in your daily work.
Read on Medium →A step-by-step guide on transitioning from medicine to cybersecurity, based on my own journey and lessons learned.
Read on Medium →I'm passionate about making security knowledge open and accessible. Whether you want to contribute to an OWASP project, invite me to speak, or just explore ideas — here's how we can work together.
Help build the Threat Model Library — the first open-source, peer-reviewed threat modeling dataset. All skill levels welcome.
I speak on threat modeling, AI in security, DevSecOps, leadership, resilience, security strategy, executive risk conversations, and building security into business decisions. Reach out on LinkedIn.
Interested in co-authoring articles, research papers, or contributing to open-source security tooling.